
Ringer
Static + live analysis of Windows kernel drivers: extract IOCTL codes and shared ring-buffer strings, then load the driver and verify every finding against the running system.
27 2Go
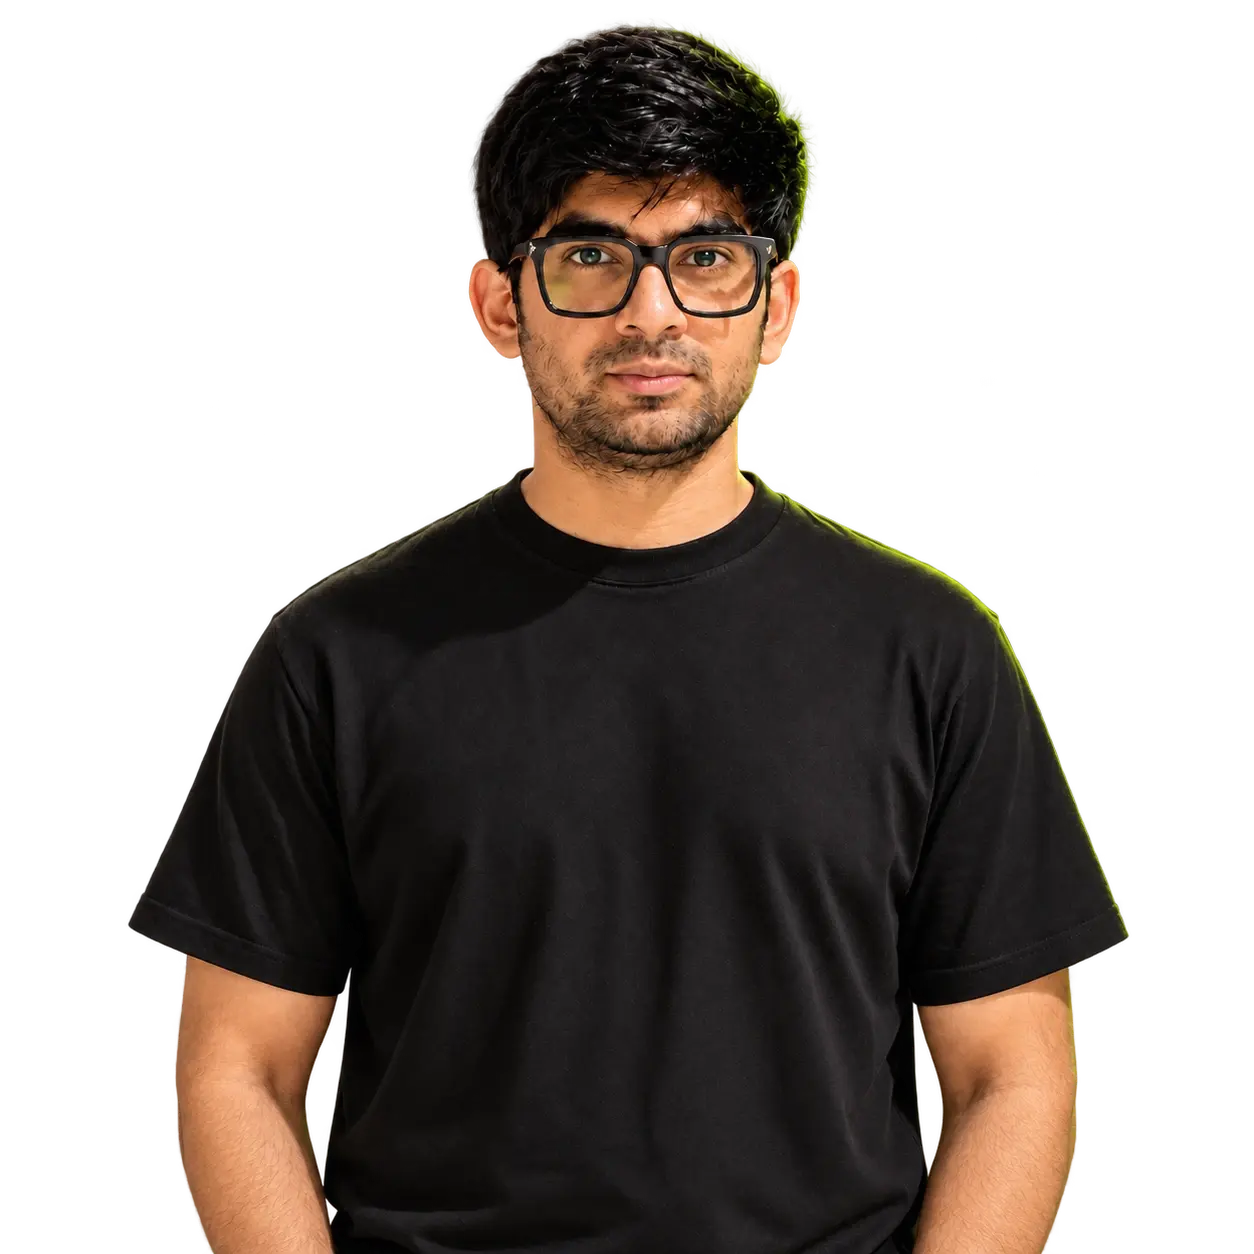
Cybersecurity researcher & developer
Researching systems, malware, and exploitation.
Exploring how systems work, break, and can be secured.
Call Sign: Sheldon · Doha, Qatar
Ideas.
Research.
Exploitation.
Understanding.

Static + live analysis of Windows kernel drivers: extract IOCTL codes and shared ring-buffer strings, then load the driver and verify every finding against the running system.

Windows process instrumentation toolkit for authorized security research, file-access manipulation, DLL search-order analysis, application resilience testing, and detection engineering.
01 / Writing
ot security
A technical analysis of OT isolation: Stuxnet, TRITON, offline malware channels, industrial protocols, WirelessHART, measurement integrity, and maintenance—with reproducible simulation labs.
kernel exploitation
A deep-dive into CVE-2025-62215 — an actively exploited race in ntoskrnl's Object Manager that double-frees the token's SID Values Block, reclaimed with a same-bucket spray and pivoted into a data-only token flip for SYSTEM.
malware analysis
Full teardown of the petshub[.]qa ClickFix campaign: a fake CAPTCHA that drops a blockchain-resolved macOS stealer and a four-stage Windows chain ending in an ACR Stealer implant flagged by 33/69 engines — Realtek masquerade, Heaven's Gate, and CVE-2024-38193 in tow.
Practical knowledge / Open reference
From reconnaissance to reporting. A field guide to offensive workflows, tools, and techniques—built for quick lookup and deeper reading.
Explore the book02 / Open source
My six most-starred projects on GitHub.
Static + live analysis of Windows kernel drivers: extract IOCTL codes and shared ring-buffer strings, then load the driver and verify every finding against the running system.

Windows process instrumentation toolkit for authorized security research, file-access manipulation, DLL search-order analysis, application resilience testing, and detection engineering.


Windows SSDT hook framework for full-spectrum syscall, file, registry, and network monitoring. Built for malware analysis and offensive security research.

03 / Publications
Post-quantum security, connected systems, and malware analysis.
NN Minhas, K Mansoor · IEEE Internet of Things Journal, 11(19), 31331-31337
NN Minhas, MW Mubeen, H Khawaja · Computer, 56(10), 31-39
N Minhas · Preprints
NN Minhas, M Naveed · IT Professional, 25(4), 21-28
N Minhas · Preprints
N Minhas, M Naveed · Preprints
W Ghazanfer, NN Minhas, M Rauf, A Anjum · IT Professional, 24(1), 56-62
04 / Expertise
05 / Experience
Red Team Operator at Cytomate Solutions and Services in Doha, Qatar. Adversary emulation, infrastructure VAPT, exploit development, and building the Psiberus autonomous simulation platform. Co-inventor on USPTO patent 18/530,422.
Built internal security tooling and hardened critical healthcare infrastructure in Pakistan. Code security audits, API security, and defensive engineering across a regulated environment.
Analysed real-world malware samples at Chunkworks in the Netherlands — reversing packers, unpacking malware families, and studying evasion techniques. Published IEEE research on post-quantum cryptography.
06 / Certifications
ISC2
Zero-Point Security Ltd
Zero-Point Security Ltd
07 / Connect
A research idea, an interesting vulnerability, or a tool worth building. Let’s talk.
Get in touch